

Ask most owners about POS security and they will tell you about hackers. Somebody in a hoodie, somewhere far away, quietly siphoning card numbers off the network. It is a real risk, and your processor spends a great deal of money making sure it stays rare. But it is almost never the thing that actually costs a small shop money.
The thing that costs you money is closer than that. It is the code taped under the register. It is the fact that every person on your staff signs in as “Manager” because that was the login the installer set up three years ago and nobody ever changed it. It is the void that happens forty seconds after a cash sale, on a Tuesday, when nobody is watching. POS security, in the way it actually matters to a business your size, is mostly a question of who can do what at your counter — and whether you would be able to tell afterwards.
The good news is that this is one of the few problems in small business that you can genuinely fix in an afternoon. Not with new hardware, not with a consultant, and not with software you have to buy. The settings are already in the system sitting on your counter. Most owners have simply never opened them.
What POS Security Actually Covers
It helps to split the phrase in two, because “POS security” gets used to mean two very different things and only one of them is your day-to-day problem.
The first half is the part your processor handles. Card data encrypted the instant it leaves the reader, tokenized so the real number never sits on your device, transmitted over channels nobody on your staff has to think about. That side of POS security is genuinely well engineered, and it is why a breach at a single-location shop is rare compared to the headlines. If you want to understand how that machinery works, tokenization is worth ten minutes of reading.
The second half is the part nobody handles for you: access. Who can ring a sale. Who can reverse one. Who can hand out a discount, open the drawer without a transaction, change a price, or pull a report that shows any of it. This is the half that decides whether your numbers mean anything, and it is where nearly all real small-business POS security failures live.
The uncomfortable framing is this: the register is not just where money comes in. It is also the only door money can leave through quietly. A stolen product leaves a gap on a shelf you might notice. A voided sale leaves nothing at all — the item is gone, the cash is gone, and your system cheerfully agrees that the sale never happened.
The Shared Login Is the Whole Problem
If you take one thing from this, take this: a shared manager code does not just weaken your controls, it erases the record. Every safeguard downstream — void reports, discount logs, drawer counts, the whole apparatus — depends on the system being able to say who. When eleven people use the same four digits, every line in every report says the same useless thing.
This is not just a best practice somebody made up. It is written into the card industry’s own rules. PCI DSS Requirement 8 asks that every individual with access gets a unique ID, and it specifically prohibits shared, group, and generic credentials — for exactly this reason. Shared accounts destroy accountability. The same requirement also says the default credentials your equipment shipped with have to be replaced, which is a polite way of saying that “1234” is not a password.
Good POS security starts with an unglamorous half hour: give every single person who touches the register their own login, delete the generic one, and change whatever the installer set on day one. You are not accusing anybody of anything. You are making the system capable of answering a question. Until it can, nothing else you do about POS security will tell you much.
There is a side benefit that has nothing to do with theft. Once every sale is attributed, your sales-per-employee numbers become real, your tip pool math stops being an argument, and your labor cost percentage can finally be measured against who was actually on the floor. Attribution is the foundation for a lot more than security.

The Four Permissions Worth Setting This Week
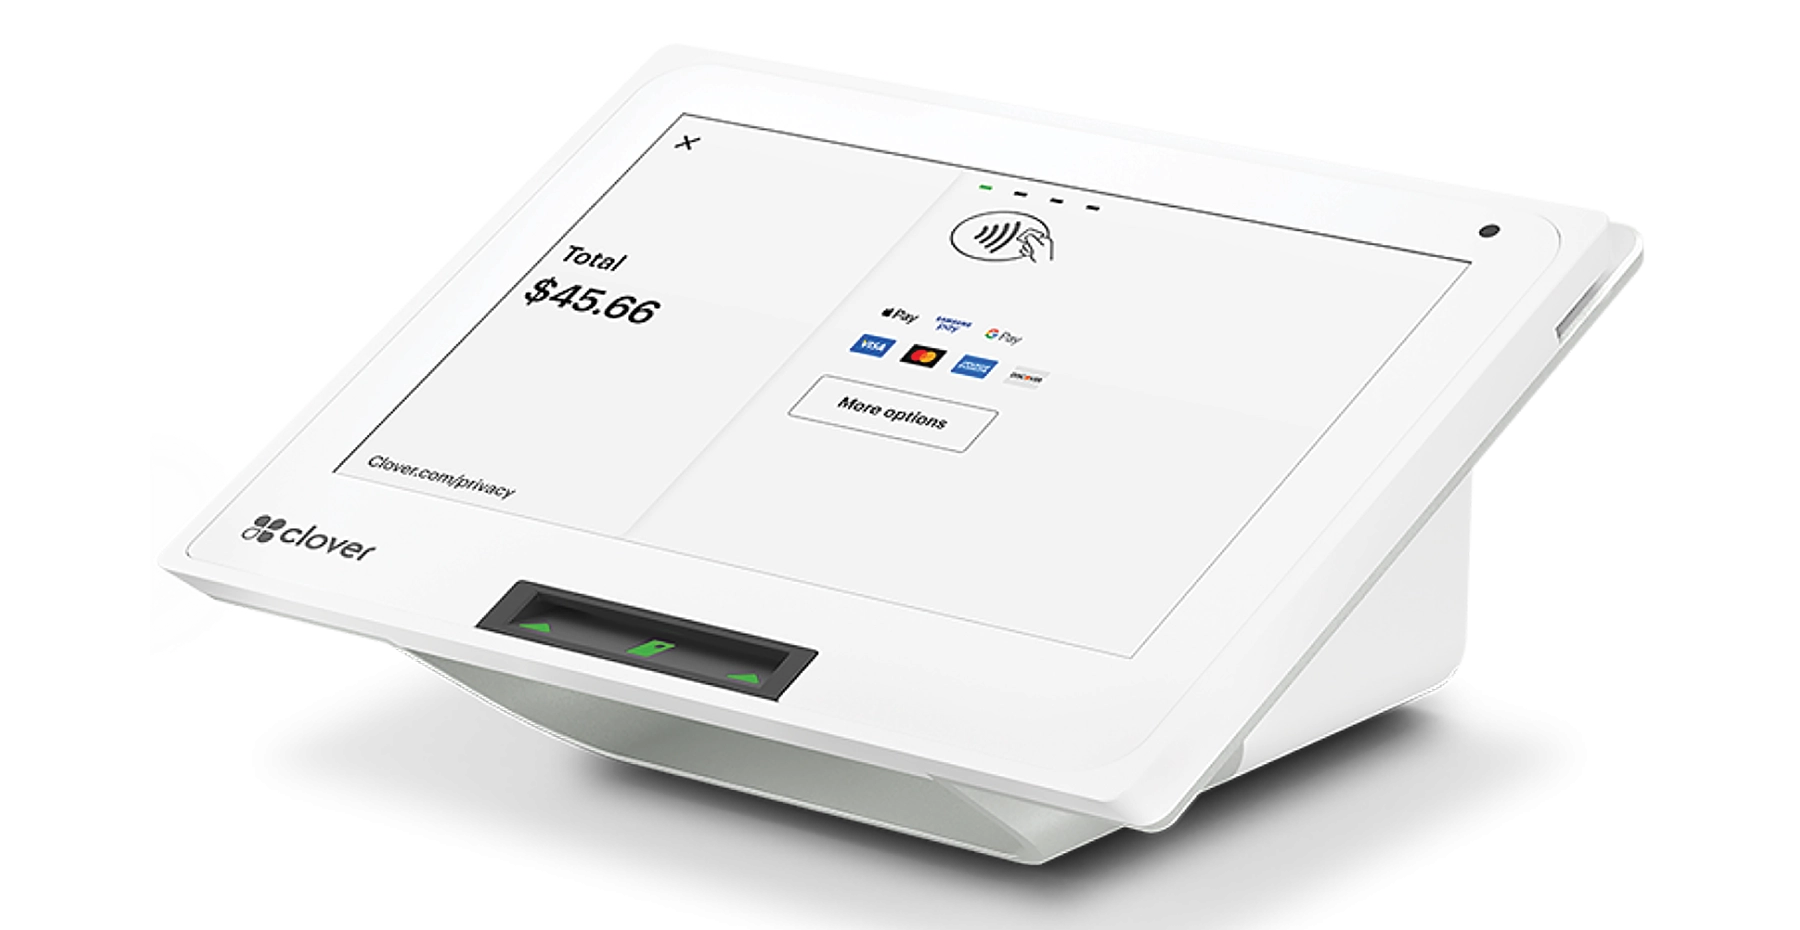
You do not need to audit forty settings. Four of them carry almost all of the risk, and on a modern system like a Clover Mini or Clover Duo each one is a toggle inside employee management. Set these four and your POS security improves more than any other hour you could spend.
1. Voids and refunds
This is the big one. A void on a completed cash sale is the cleanest way money leaves a small business, because it removes the evidence along with the money. Restrict voids and post-sale refunds to a named manager login — not a shared code, a named one — and require that login every time. If your system can force a reason code on a void, turn that on too. Most people will never think about it again. The one person who was thinking about it will.
2. Discounts and comps
Discount abuse is quieter than a void and usually larger in aggregate. It is also the one that most often is not theft at all — it is a well-meaning employee discounting a friend’s order, every shift, for a year. Cap the discount a regular login can apply, either as a percentage or a dollar amount, and send anything above it to a manager approval. You will find out fast whether your comp policy is a policy or a habit.
3. No-sale drawer opens
Opening the drawer without a transaction is legitimate — making change, correcting a miscount, dropping cash. It is also the simplest possible move if the intent is otherwise. Most systems can log every no-sale open against a user, and some can require an approval. If your cash drawer comes up short on a regular basis, the no-sale log is usually where the pattern shows first.
4. Price edits and settings
Almost nobody on a shop floor needs the ability to change an item’s price, edit the item list, or alter tax settings on the fly. Lock those to the owner and one trusted manager. The upside is bigger than POS security alone: your item list stays clean, which means the numbers in your reports stay clean, which is the entire premise of using a barcode scanner and of tracking retail metrics in the first place.
None of the four requires you to distrust your staff. They require you to build a counter where a mistake is visible and a bad decision is inconvenient. That is what POS security is for.
POS Security Has a Hardware Half Too
Permissions cover the inside. The hardware half of POS security covers what happens to the physical device on your counter, and it comes down to four habits that take less time than restocking a shelf.
Look at your reader. Once a week, actually look at the card slot and the tap surface. Skimming overlays are designed to be unremarkable, so what you are checking for is change — a slot that sits slightly proud, a seam that was not there, a panel that flexes, adhesive residue, a device that suddenly feels loose on its base. You know what your own terminal looks like better than any checklist does.
Take updates when they come. The update notice that appears at the worst possible moment is not an inconvenience, it is the patch. On a cloud-connected system the updates arrive on their own, which is one of the quieter arguments for a modern POS device over an old standalone terminal that has not been touched since installation.
Put the register on its own network. If your guest wifi password is on a chalkboard, your POS should not be on that network. Most routers will run a separate network in about five minutes. It is the single highest-value technical step in small-business POS security and it costs nothing.
Know what happens when the internet drops. Outages happen, and how your system behaves during one is a POS security question as much as an operations one. Understand your offline processing limits before you need them, rather than discovering them during a rush.
Worth saying plainly: none of this replaces PCI compliance, and PCI compliance does not replace any of this. If the annual questionnaire is a thing you click through without reading, the PCI basics are worth an honest read — the questions map almost exactly onto the habits above.

What the Numbers Say About Where Losses Come From
The National Retail Security Survey — the long-running industry benchmark the National Retail Federation ran with the Loss Prevention Research Council — put shrink at 1.6% of total retail sales, roughly $112.1 billion, with theft in both directions accounting for close to two-thirds of it. The rest is process failure and administrative error, which is its own argument for tight permissions.
The figure worth sitting with is the internal one. The same research put the average loss from a single investigated internal theft at about $2,180. Not a career of skimming — one investigated incident. Run that against a shop doing $600,000 a year and you are looking at roughly four days of revenue evaporating from a single case that the owner, by definition, only found out about after the fact.
Two honest caveats. That survey is not published annually any more, so treat those numbers as a benchmark rather than this quarter’s reading. And the averages come from retailers far larger than yours. But the direction is the point, and the direction is not subtle: a meaningful share of retail loss walks in through the front door with a name tag on. POS security that only looks outward is looking the wrong way.
The Ten-Minute Weekly Check
Settings decay. Staff turn over, a permission gets loosened during a busy December and never gets tightened, a temporary login outlives the temp. The fix is not vigilance, which nobody can sustain. It is a short recurring look at four reports your system already produces.
| What to look at | Where it lives | What a bad answer looks like |
|---|---|---|
| Voids and post-sale refunds | Transaction or void report, filtered by employee | One name well above everyone else, or voids clustered at quiet hours |
| Discounts and comps | Discount report by employee | A steady discount rate that never varies, or one login applying most of them |
| No-sale drawer opens | Cash or drawer activity log | Opens that do not line up with shift changes or making change |
| Active logins | Employee list in your dashboard | Anyone who no longer works for you, or a generic account you thought was deleted |
Ten minutes on a slow afternoon. You are not hunting anybody — most weeks you will find nothing, which is exactly the outcome you want. What you are really doing is making it known that the reports get read, and a counter where the reports get read is a very different counter. Your dashboard already builds every one of these; nobody ever told you to open them.
One more line item belongs on that list, and it is the one most owners skip: remove logins the day someone leaves, not the month after. A former employee’s credentials are the most common gap in small-business POS security, and it is entirely an administrative one. The same discipline applies to time clock access and anything else tied to that person.
Where the Outside Threats Still Fit
None of this means external risk is imaginary. It means it arrives through different doors, and mostly not through the register. Card-not-present orders carry a fraud rate several times higher than anything at your counter, which is why card not present fraud deserves its own playbook if you sell online or take orders by phone. Disputes are their own discipline — chargeback prevention starts long before a dispute is filed. And refunds at the counter have a fraud pattern all their own, covered in return fraud.
Data is the other outside door. If you keep customer records, the safest record is the one you never collected — a principle that runs through both protecting your business from identity theft and the way you build a customer database. Complete POS security means the inside doors and the outside ones, in that order of likelihood.
It is also worth training on. New staff learn the register in their first week and never revisit it, which is when habits calcify. Folding permissions and reason codes into POS training costs nothing and makes the rules feel like the job rather than an accusation. Shops in higher-risk categories — a smoke shop, a busy quick-service counter, a salon with independent operators — get the most out of doing this early.
Not sure what your POS security settings are actually set to?
VMS will walk your permissions, logins and reports with you and lock down the gaps — usually in one short call, at no cost.
Or call our team: 888-902-6227
Good POS Security Is Mostly Housekeeping
There is no product that fixes this, which is probably why nobody sells it to you. POS security at a shop your size is unique logins, four permissions set deliberately, a weekly ten-minute look at reports that already exist, and a quick glance at the hardware on your counter. That is the whole list. It is housekeeping, and like all housekeeping the hard part is starting rather than doing.
What you get back is worth more than the losses you avoid. Numbers you can trust. A staff that knows where the lines are, which is a kindness rather than a threat. And the ability to answer “who did that” with a name instead of a shrug — which, on the one day it matters, is the difference between a conversation and a guess.
If you are not sure where those settings live on your system, that is normal, and it is a ten-minute call rather than a project. VMS sets up POS systems for small businesses every day, and we will go through your permissions, your logins and your reports with you — and while we are in there, take an honest look at what you are paying to accept cards. Plenty of owners find that Zero Fee Processing pays for the whole upgrade. Have a look at the merchant services FAQs, see who we are, or just get in touch. Tightening POS security is one of the few things on your list that gets easier the sooner you start.
Have questions about POS security?
Fill out the form below and a VMS payment specialist will contact you shortly.